
Built in
- Honeypot: a hidden field that bots fill in and people do not. Applies to everyone except agents.
- Rate limit: limits how many tickets one person can send in a set time, counted by IP address. It applies to guests and logged-in customers. Agents are exempt.
- Security check: a hidden token on the form that guests must pass. It is why you should keep your support pages out of page caching.
Set the rate limit
- Go to Helpdesk > Settings and find the "Ticket Assignment" section.
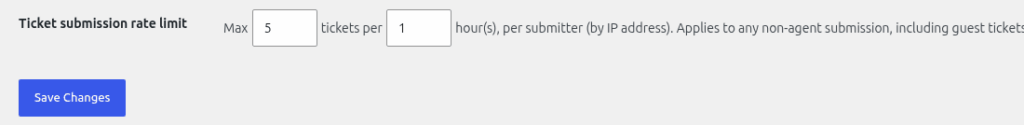
- Find "Ticket submission rate limit". It reads "Max [5] tickets per [1] hour(s), per submitter (by IP address)".
- Change the two numbers and click that section's "Save Changes" button.
The default is 5 tickets per 1 hour. The lowest value is 1, so the limit cannot be switched off: 0 or a blank box is saved as 1. A customer who goes over sees "You have submitted too many tickets recently. Please try again later."
If your site sits behind a proxy or CDN, every visitor can look like the same IP address. A developer can fix this with the wphd_submitter_ip filter.
CAPTCHA
HelpDesk WP has no built-in CAPTCHA and no ready-made link to reCAPTCHA or Turnstile. A developer can add one: show the field with the wphd_ticket_form_before_submit action, pass the token along with the wphd_rest_create_ticket_data filter, and check it in the wphd_ticket_submission_allowed filter. See "Developer guide: REST API, hooks and events".
Still stuck? Open a ticket on the support page on ABC and a real person will help.
Was this article helpful?